A platform to govern compliance and risk

Prometeo is the GRC (governance, risk and compliance) platform we designed for our clients. It brings together in a single repository what is usually scattered across spreadsheets, folders and emails: requirements, risks, suppliers, evidence, deadlines.
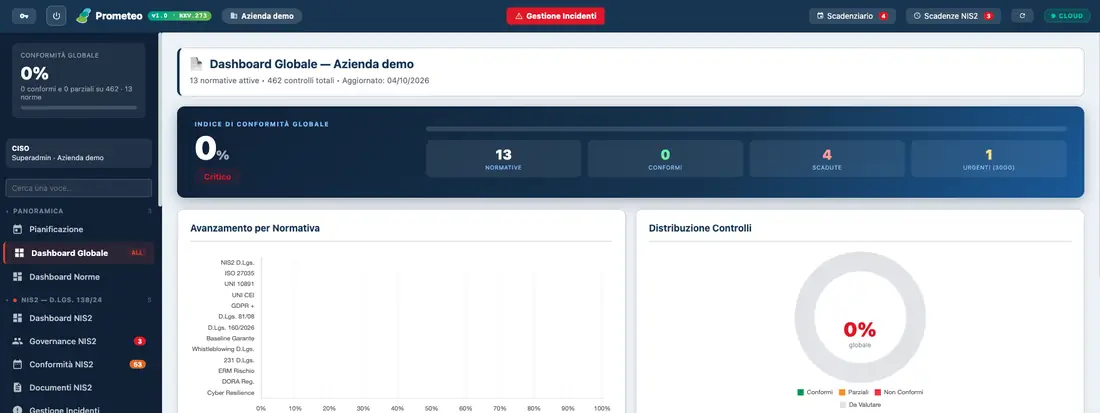
Prometeo global dashboard: compliance index, active regulations, progress by regulation and distribution of controls
Global dashboard of a demo company: 13 active regulations and 462 controls in a single view.
How it works

One object, one repository, many views

Each piece of information is entered only once: a supplier, a service, a risk, a finding. The same information then serves NIS2, ISO/IEC 27001, the 231 model and enterprise risk management, with no duplicate entries and no conflicting versions.

The client works on its own data, fills in the assessment checklists and uploads the evidence. We follow all clients from a separate supervision panel, from which we activate the standards and modules each one needs: if a standard is not active, the related menu simply does not appear.

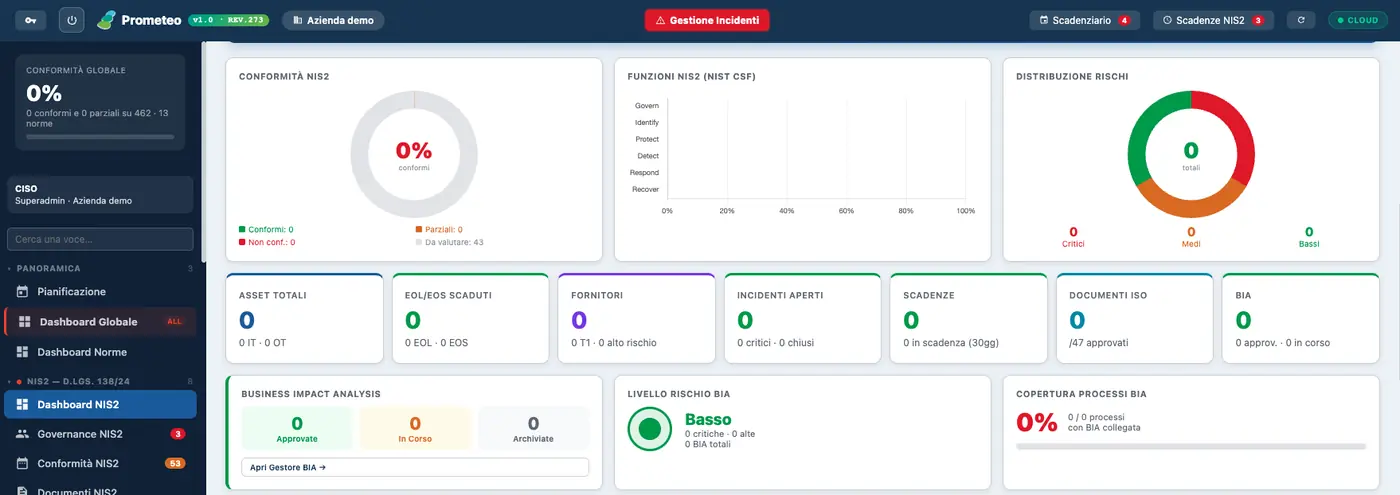
  • NIS2 security measures according to the ACN determinations, with an assessment checklist filled in by the client
  • ISO management systems on the Harmonized Structure: common requirements are assessed once for all active standards
  • Business impact analysis (BIA), even more than one for the same service, risk register and treatment
  • Relevant suppliers, services, platforms and findings linked to one another
  • A single schedule for obligations, documents and notifications
  • Regulatory watch to follow new determinations and changes to the standards
Prometeo diagram: a single repository with assets, suppliers, services, risks, findings, evidence, documents and deadlines, connected to the governance, compliance, risk and continuity, incidents, audit and printing modules; the client works on its own data, the Supervisor follows all clients
The views

From the summary for top management to operational detail

The modules

What’s inside

Modules are activated per client, based on the standards that apply to it.

Governance and planning

  • Activity planning
  • Global and per-standard dashboards
  • NIS2 governance: roles, delegations, resolutions
  • Schedule

Compliance and documents

  • NIS2 compliance with the ACN measures
  • Documents and approvals
  • ISO certificates
  • GDPR, Legislative Decree 81/08, 231 model

Risk and continuity

  • Enterprise Risk Management
  • Business impact analysis (BIA)
  • Organisation, assets and systems
  • Suppliers and supply chain

Incidents and resilience

  • Incident management with notification deadlines
  • Exercises
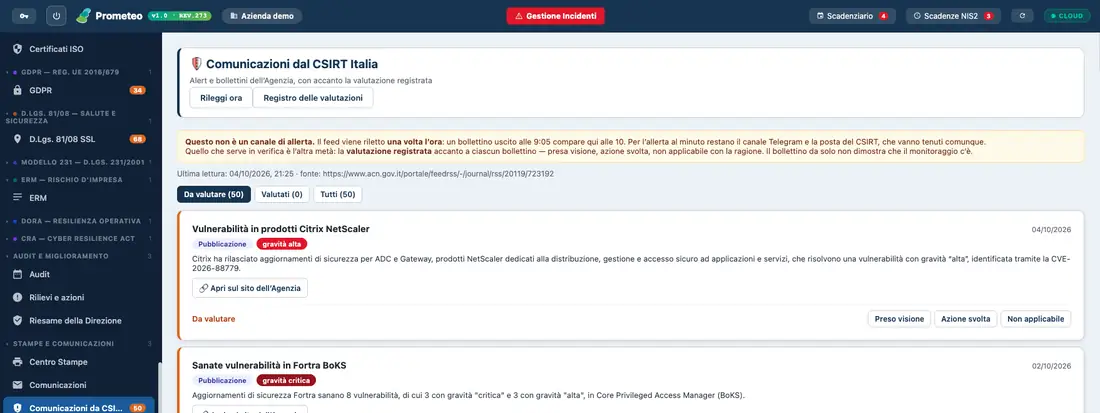
  • Communications from CSIRT Italia
  • Mapping of cyber scenarios, DORA, Cyber Resilience Act

Audit and improvement

  • Audit
  • Findings and corrective actions
  • Management review
  • Cyber KPIs and training

Printing and communications

  • Print centre for reports and documents
  • Communications to corporate bodies and functions
  • Whistleblowing channel (Legislative Decree 24/2023)
Standards and schemes

What it covers

NIS2 and PSNC

Legislative Decree 138/2024 and ACN determinations, incident notifications, management bodies, suppliers.

ISO standards

ISO/IEC 27001 and the 27000 family, ISO/IEC 27035, ISO 22301, ISO/IEC 20000-1, ISO/IEC 42001, ISO 9001, with a common assessment of clauses 4–10.

231 and ERM

Predicate offences, protocols and enterprise risk as a whole, not just cyber.

Privacy and artificial intelligence

GDPR, the Garante’s baseline of controls, Legislative Decree 160/2026 on artificial intelligence.

Specific sectors

UNI 10891 and UNI CEI EN 50518 for private security and monitoring centres, the Italian Coast Guard circular on maritime cyber risk, Legislative Decree 81/08.

Finance, products and managed services

DORA, Cyber Resilience Act and preparation for the ENISA EUMSS European scheme for managed security services, currently in draft.

How we work

Prometeo within an engagement

Prometeo is not sold on its own: we use it within a consulting engagement, CISO as a Service or NIS2 support. The platform holds the work together; decisions remain with the organisation.

  1. Activation. Together we choose the standards and modules that apply to the organisation.
  2. Inventory. Organisation, services, assets, suppliers and existing documents are entered only once.
  3. Assessment. The client fills in the checklists and uploads the evidence; we verify it.
  4. Action plan. Findings, corrective actions, owners and deadlines, visible to those who must decide.
  5. Monitoring. Schedule, CSIRT bulletins, management review and reports for the management bodies.

Want to see it at work?

Write to us and we will show you how we would use it for your organisation, on a demo company and not on other clients’ data.

Request a demo