About us
The rules change.
Experience makes them workable.
NIS2, ISO/IEC 27001, GDPR, National Cyber Security Perimeter: for many organisations information security has become a list of obligations. 823 Consulting is the link between the two worlds: what the rules require and what a company can actually do, with the people and the budget it has.

Who 823 Consulting is
823 Consulting is the consultancy founded by Giacomo Pesce in 2017. We work in information security, risk management, business continuity and data protection, with a practical approach: risk first, then documents.
We work for public and private organisations, from small businesses to NIS2 essential entities. For services that require shifts, tools and dedicated people we work with specialist partners.
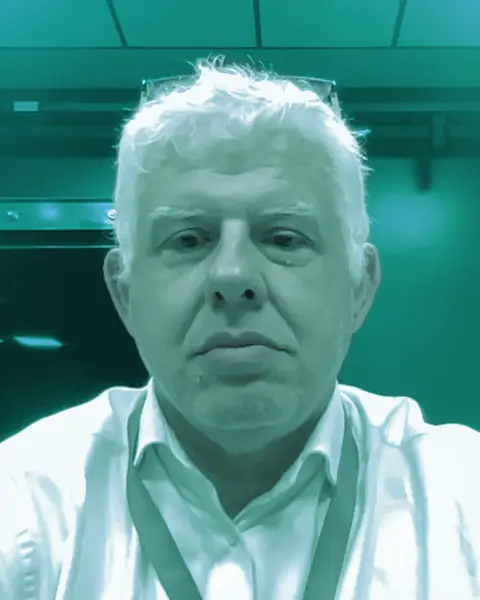
Giacomo Pesce
Founder · CISO, DPO and ISO/IEC 27001 Lead Auditor
He started working in 1987 as a developer and technician, when company networks were built one cable at a time and the web was about to be born. In 1996 he built the first integrated management system on a local network and began working on the Internet, creating the first Internet POPs in Liguria and the first internet café in Italy. From there, information security, risk management and management systems became his work.
Since 2005 he has worked on business risk analysis and management; in 2010 he became an ISO/IEC 27001 Lead Auditor. He has also held the role of General Manager in national and international companies.
Today he is Chief Information Security Officer of an entity included in the National Cyber Security Perimeter (PSNC). The rules we help to apply, he applies first of all himself, every day.
Where it all began
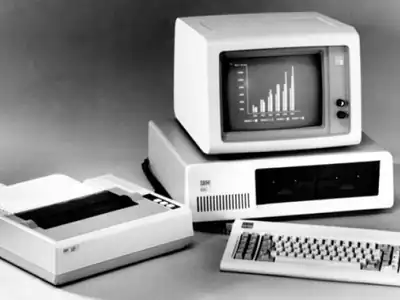
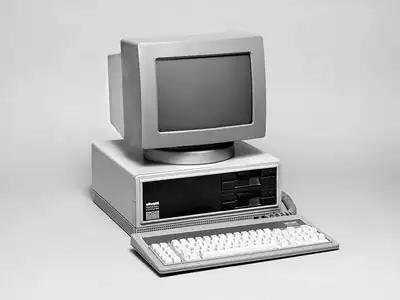
On 30 April 1993 CERN in Geneva put the World Wide Web software into the public domain: the “line-mode” client, the server and the common code library. From that day anyone could use it, modify it and redistribute it: it is the document that made the web everyone’s.
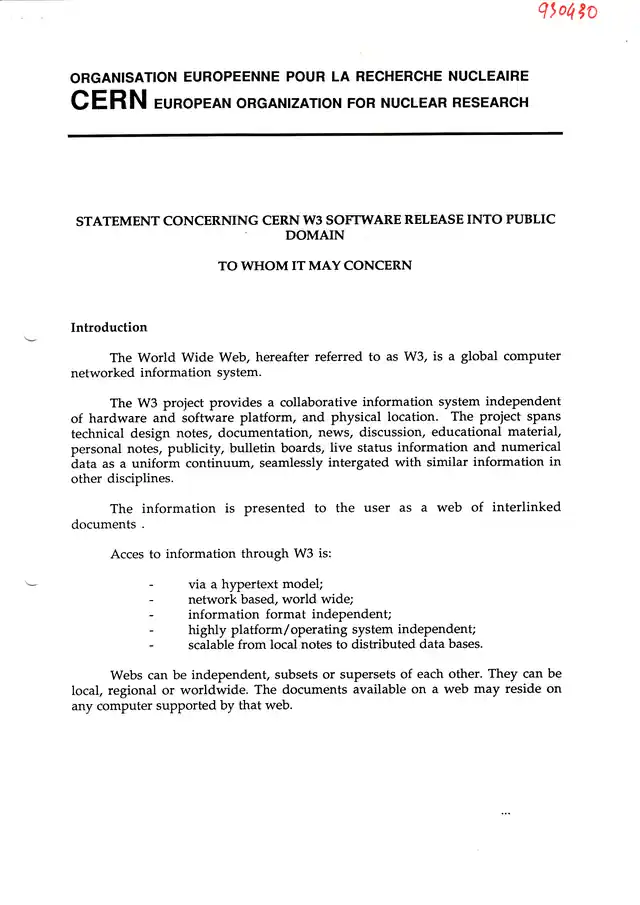
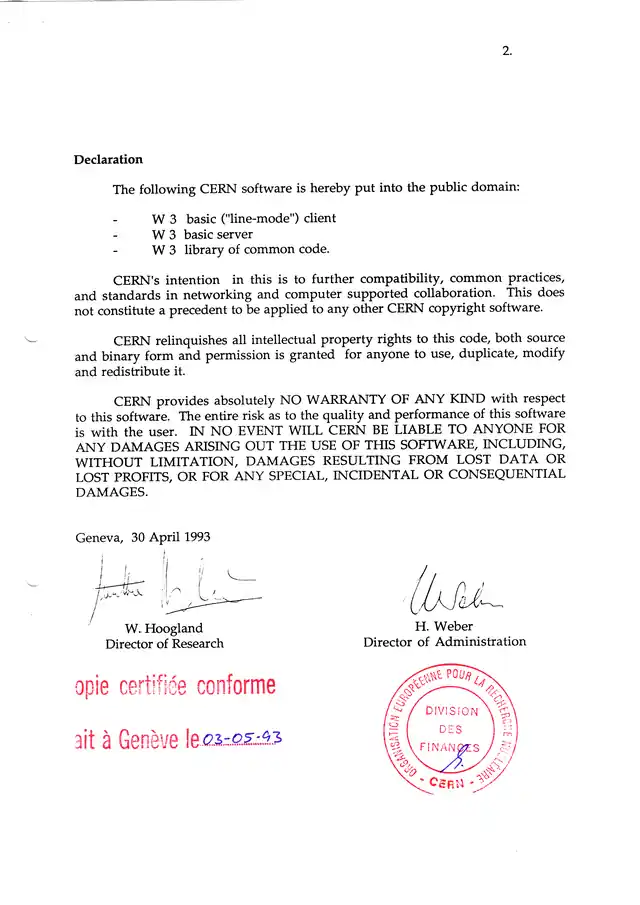
CERN, “Statement concerning CERN W3 software release into public domain”, Geneva, 30 April 1993 (certified true copy of 3 May 1993).
Skills and method: security first
ISO/IEC 27001 Lead Auditor
TÜV SÜD (2010) and ACM CERT (2017) certificates. Courses recognised by AICQ SICEV.
Qualified trainer
Qualified ISO/IEC 27001 trainer for DNV and Kiwa. Trainer on Lean Six Sigma programmes.
Data Protection
DPO appointments and certifications as Data Protection Auditor and Data Protection Officer (DPO).
Risk first, then documents
A procedure that nobody applies is one more risk, not one less.
Honesty
If something is not needed, or if we are not the right people to do it, we say so straight away.
Client autonomy
We leave behind tools and skills that stay in the company, not dependence on the consultant.
There when you need us
For a project, an assessment or an ongoing incident: the first conversation is to understand whether it makes sense to go ahead, for both of us.