
Port facilities: MIT Circular 177/2025
From 1 November 2026 cyber risk enters the PFSA and the PFSP: CyPFSO, training, joint cyber drill and incident reporting to the MIT as well.
823 Consulting is the consultancy of Giacomo Pesce, CISOaaS and CISO in companies within the National Cyber Security Perimeter (PSNC). We bring the same experience to companies that need to become compliant and stay operational.

Before that: CSIRT contact person by 31 December 2026 and notification of significant incidents from 1 January 2027. The full timeline →
With Prometeo we manage the organisation’s NIS2 measures and the Cyber Resilience Act compliance of its products in the same repository.
Discover PrometeoPorts, automotive, food and beverage and healthcare, plus NIS2 and the Cyber Resilience Act: the cyber rules that are coming, what they require and by when.
From 1 November 2026 cyber risk enters the PFSA and the PFSP: CyPFSO, training, joint cyber drill and incident reporting to the MIT as well.

Manufacturers ask suppliers for ISO/SAE 21434 and TISAX evidence; NIS2 and the CRA add legal obligations, with CRA reporting already from 11 September 2026.

Food production, processing and distribution fall under NIS2 and the CER Directive; from 2027 the Machinery Regulation brings cybersecurity to the production lines.

Hospitals, health authorities, laboratories and pharmaceuticals are among the sectors of high criticality under NIS2. Networked medical devices, health data and continuity of wards: what the rules require and where to start.
Since 11 September 2026 actively exploited vulnerabilities and severe incidents are reported to ENISA; requirements and CE marking from 11 December 2027. The status in November and what to do now.
CSIRT contact person by 31 December 2026, incident notification from 1 January 2027, baseline measures by 31 July 2027: the timeline and the order in which to tackle it.
We work where regulatory compliance and operational security meet: not documents to file away, but decisions to make and to be able to defend before senior management and the authorities.
An information security officer without hiring one full time: strategy, risk, suppliers, relationship with the board.
Learn more →From the applicability check to compliance with the ACN baseline measures, with incident notifications already tested.
Learn more →CSIRT as a Service and incident response with specialist partners, plus “War Room” exercises to train the crisis committee.
Learn more →Appointment as Data Protection Officer (DPO), data protection impact assessments (DPIA), records, data breach management.
Learn more →ISO/IEC 27001 and the 27000 family, ISO 22301, ISO/IEC 20000-1, ISO/IEC 42001: design, internal audits, support through certification.
Learn more →Courses for auditors and managers, training for executives and management bodies on NIS2, risk and business continuity.
Learn more →Reporting channel compliant with Legislative Decree 24/2023 and the ANAC Guidelines: encrypted platform, independent external manager, procedure, privacy notices and training.
Learn more →Giacomo Pesce started in 1987 as a developer and technician. In 1996 he built the first integrated management system on a company network, when many of the standards we apply today did not yet exist, and in the same year he launched himself into the still unknown web.
Since then he has worked in information security, risk management and management systems. Today he is a CISO, DPO and Lead Auditor: our team works both for those who must protect and for those who have already been hit and do not know how to manage the incident.
The journey
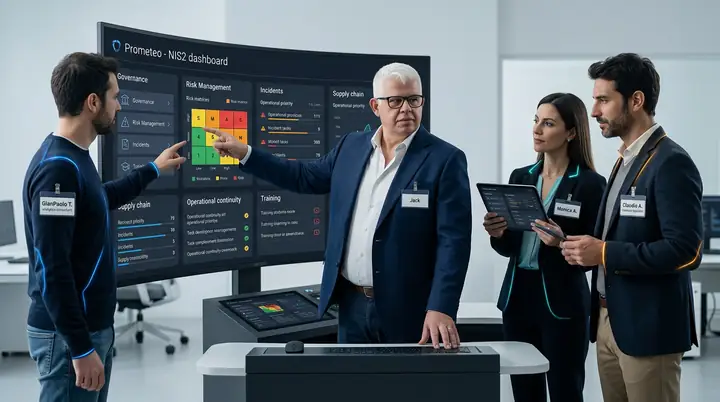
Prometeo is the GRC platform we developed and use with our clients. For NIS2 it covers ACN measures, management bodies, suppliers, incidents and notifications; for the Cyber Resilience Act the product inventory, the Annex I requirements product by product, the SBOM, vulnerabilities and Article 14 reports. The same information also serves ISO/IEC 27001, 231 and risk management, with no duplicate entries.
The platform organises the work and the evidence; decisions and compliance remain with the organisation.
Some services require shifts, tools and dedicated people. For these we work with partners whose work we know closely.
Managed Service Provider specialising in data centres: hosting, cloud, colocation, migrations and management of digital infrastructure.
With us: Giacomo Pesce is CISO and DPO of Momit; together we offer CISO as a Service and CSIRT as a Service.
momit.eu →
Compliance, risk analysis and definition of controls in IT, OT and artificial intelligence; cyber security, cloud and disaster recovery solutions; managed services and training.
With us: information security services, training and incident response.
cloudsecurityitalia.it →
Lean Six Sigma training, coaching and consulting, from Yellow Belt to Master Black Belt programmes, to improve processes with measurable results.
With us: training programmes on process improvement and the Lean Six Sigma methodology.
theleansixsigmacompany.it →
European data centre operator: colocation with dedicated racks and cages, redundant connectivity with over 60 peering carriers and 24-hour on-site technical services, with campuses in Sweden, Norway, Denmark, Switzerland, Italy (Milan) and Spain.
With us: management of client data and cloud infrastructure fully managed by Momit.
vaultica.com →
Law firm based in Varese focused on digital law: commercial and ICT law, data protection and privacy, artificial intelligence and new technologies, Cyber Resilience Act.
With us: the legal side of privacy, ICT contracts, the Cyber Resilience Act and artificial intelligence.
studiolegalebroglia.com →Do not switch everything off and do not delete anything. Call us: the sooner the evidence and the notification deadlines are put in order, the better.